Security
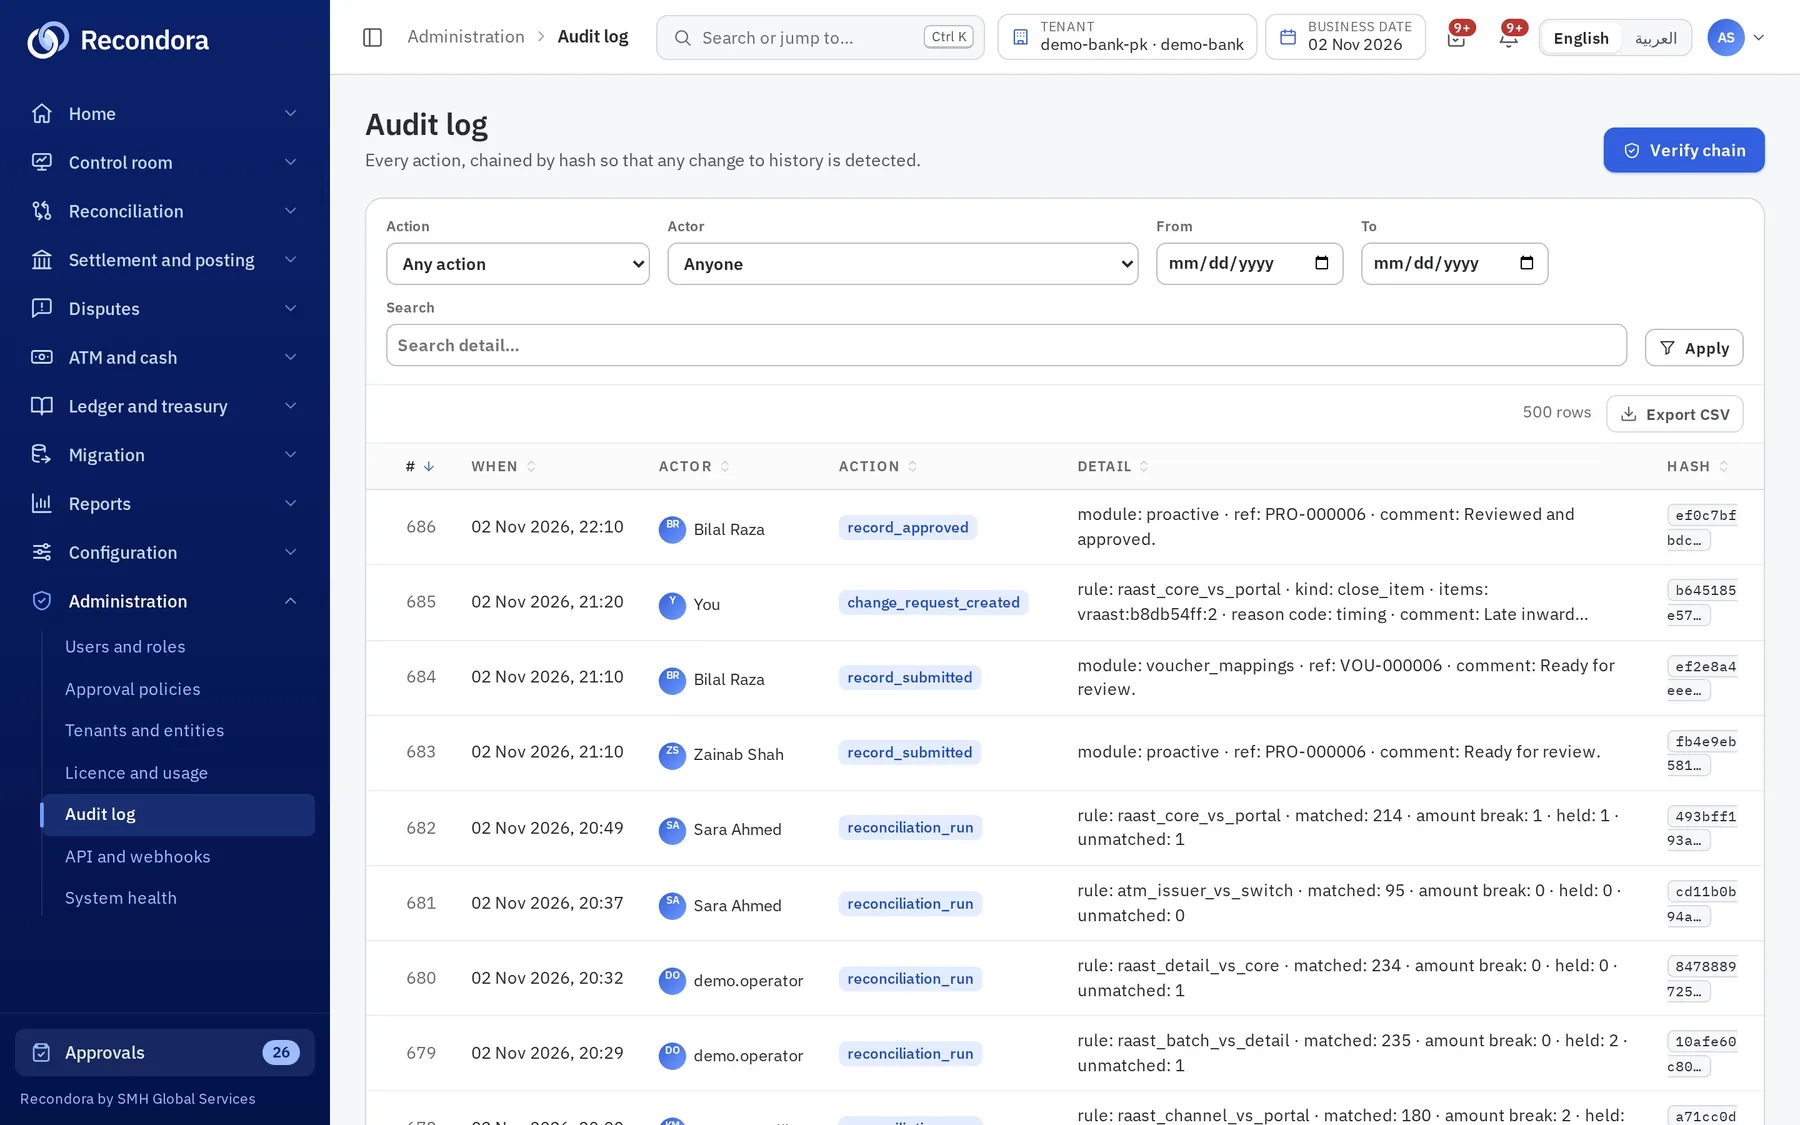
No certification claimed until it is audited
Controls are mapped today; certification comes only after an independent audit.
Assurance roadmap
What is mapped, tested and targeted
- Controls mapped to PCI DSS, ISO/IEC 27001, NIST CSF 2.0 and the SAMA, NCA, SBP and Bangladesh Bank frameworks (R1).
- Independent penetration test before every major release.
- ISO/IEC 27001 gap assessment (R2); ISO/IEC 27001 certification of the SaaS service and a SOC 2 Type II report targeted for R3 (Q1 2028).
- PCI DSS applicability assessed per deployment; the design keeps full card numbers out.
Reporting a vulnerability
Write to info@smhglobal.com.pk with the subject "Security". Please do not test against customer environments. We acknowledge reports within two working days and keep you informed until the issue is fixed.
See it with your own files.
Book a walkthrough: we load sample files from two of your rails, run them through Recondora and show you every match, break and approval.